Microsoft Intune helps IT teams manage devices, deploy applications, and protect company data from a central cloud service. It is particularly useful for organisations that use Microsoft 365 and need to support employees working across different locations and device types.
However, choosing Intune involves more than comparing subscription prices. You also need to understand platform differences, app protection, security integrations, and which advanced features your existing licenses include. This article explains the main capabilities, current pricing, and practical considerations when evaluating Intune.
Contents
What is Microsoft Intune?
Microsoft Intune is a cloud-based endpoint management service. Administrators use the Microsoft Intune admin center to manage device settings, applications, compliance, and access to organisational data.
Intune supports two different management approaches:
| Approach | Purpose | Example |
|---|---|---|
| Mobile Device Management (MDM) | Manage an enrolled device and its configuration. | Apply security settings and deploy apps to a company laptop. |
| Mobile Application Management (MAM) | Protect organisational data inside supported apps. | Restrict copying work email to personal apps on an employee’s phone. |
You can combine MDM and MAM. A company-owned phone can be enrolled in Intune and also receive app protection policies. For supported BYOD scenarios, app protection can protect work data without enrolling the entire device. Microsoft Entra ID provides the identities and groups used with Intune. Administrators assign policies and applications to appropriate users or devices through Entra groups.
Supported platforms
Microsoft Intune supports multiple operating system platforms, including Windows, macOS, iOS/iPadOS, Android, Linux, and Chrome OS. However, the available management features vary depending on the platform. For example, device enrollment methods, configuration policies, remote actions, and app protection capabilities may not be the same across all operating systems.
Before enrolling devices in Intune, check the supported operating system version, edition, device type, and management requirements. For Linux devices, verify that the distribution and desktop environment are supported. Chrome OS devices have more limited management capabilities, and Intune app protection policies are not supported on Chrome OS.
For more information about supported platforms and operating system requirements, refer to the official Microsoft documentation: Operating systems and browsers supported by Microsoft Intune – Microsoft Intune | Microsoft Learn.
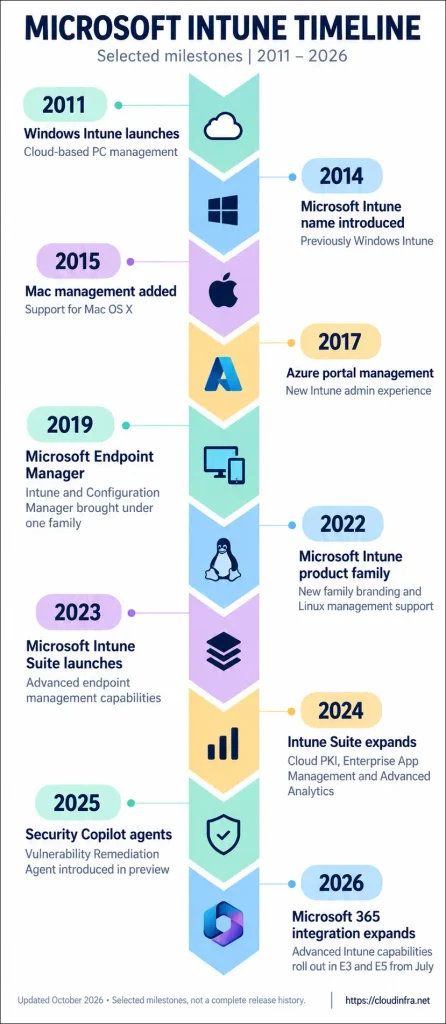
Microsoft Intune Timeline
The image below shows the Microsoft Intune timeline from 2011 to 2026. It does not include every feature released during this period but instead highlights the most important milestones across the different years.
Key Microsoft Intune Features
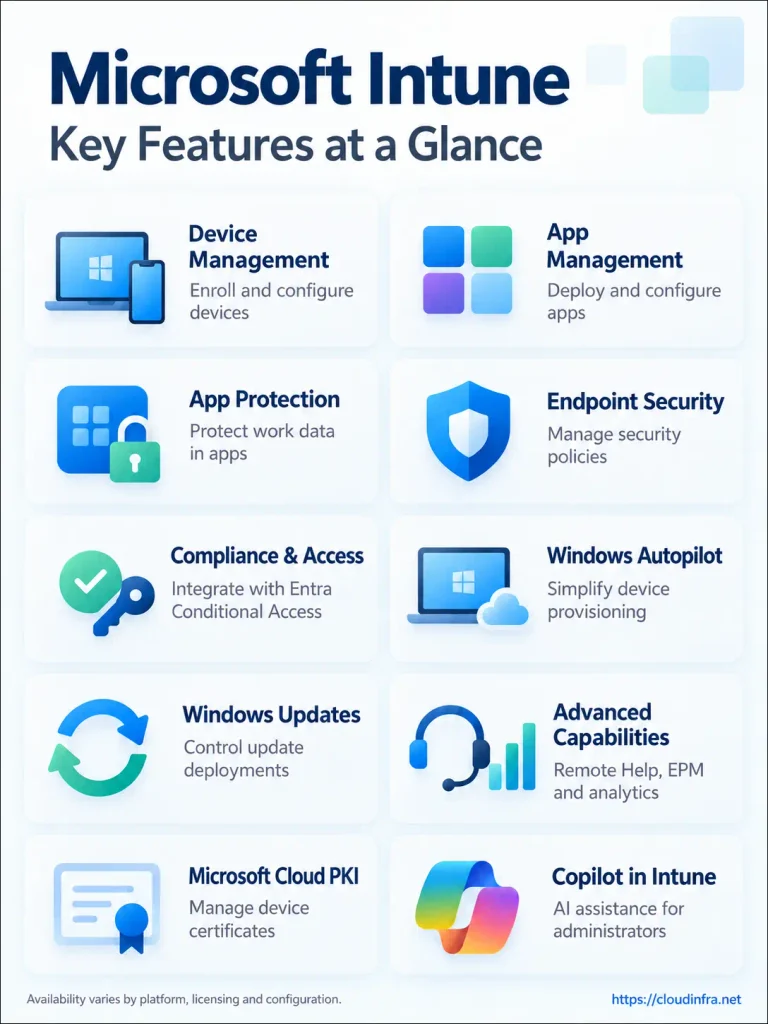
- Mobile Device Management (MDM)
- Mobile Application Management (MAM)
- Endpoint Security
- Autopilot
- Autopilot Device Preparation
- Windows Update for Business
- Intune Cloud PKI
- Embedded Security Copilot Experience
1. Device Enrollment and Management (MDM)
Mobile Device Management (MDM) allows IT administrators to configure, manage, and maintain enrolled devices throughout their lifecycle. The enrollment method you choose depends on the device platform, whether it is company-owned or personally owned (BYOD), and whether it is used by a single user or shared among multiple users.
When evaluating an MDM solution like Microsoft Intune, test the features that are important to your organisation. These include device enrollment, configuration policy deployment, application installation, compliance reporting, and device removal. You should also check which remote actions are supported on each platform, such as restart, rename, retire, and wipe, as not all actions work the same way on Windows, macOS, iOS, and Android devices.
I recommend testing with both a new device and an existing device. This helps you understand the differences between enrolling a brand-new device and bringing an already-used device under Intune management.
Refer to the post to start with your Intune MDM setup Initial Setup Of Microsoft Intune MAM/MDM [12-Steps].
2. Application Deployment and Configuration
Microsoft Intune allows IT administrators to deploy, configure, and manage applications across supported platforms, including Windows, macOS, iOS, and Android. Administrators can assign applications to users or devices, configure supported application settings, and monitor installation status from the Intune admin center.
The application types and deployment methods vary depending on the operating system. For example, deploying a Windows application may require different packaging, installation commands, and detection rules compared to deploying an application on an iOS or Android device.
It is also important to understand the difference between application deployment and app protection policies. Deploying an application does not automatically protect the data within it. Similarly, applying an app protection policy does not automatically install the application on a device. These are separate features in Intune that can be used together to manage applications and protect corporate data.
When testing application deployments, verify that applications install successfully, assignments target the correct users or devices, and installation status is reported correctly. You should also test how applications are updated, uninstalled, or removed when they are no longer required.
3. App Protection for Personal Devices (MAM)
Microsoft Intune App Protection Policies (MAM) help IT administrators protect corporate data within supported applications, even when a device is not enrolled in Intune. Depending on the operating system and application, administrators can configure policies to require an app PIN, restrict copy and paste, prevent company files from being saved to personal storage locations, and selectively remove corporate data from managed applications.
One important feature is MAM selective wipe, which allows administrators to remove company data from supported applications without uninstalling the applications or factory-resetting the device. This is particularly useful when an employee leaves the organization or no longer requires access to corporate data.
For example, an employee can use Microsoft Outlook on their personal iPhone or Android device to access work emails. Intune app protection policies can protect the corporate account and its data while keeping the employee’s personal information separate.
However, MAM without device enrollment has some limitations. Unlike Mobile Device Management (MDM), it does not provide full control over device settings, security configurations, or operating system features. Users are also generally responsible for downloading and installing the required applications themselves.
Refer to the link to read more about app protection policies: App Protection Policies Overview – Microsoft Intune | Microsoft Learn.
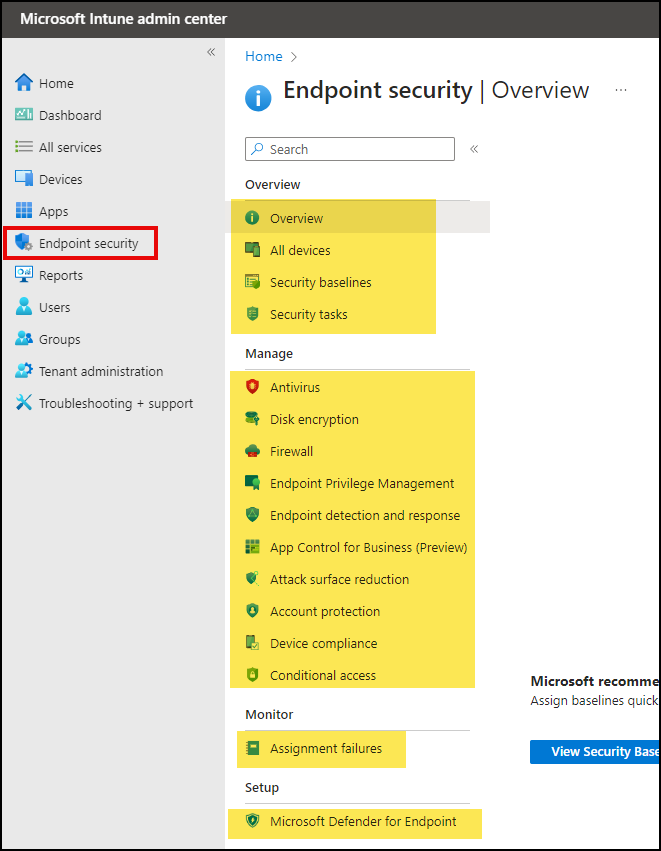
4. Endpoint Security Policies
Microsoft Intune provides endpoint security policies and security baselines that help IT administrators protect and secure managed devices. These policies can be used to configure important security features such as Microsoft Defender Antivirus, disk encryption (BitLocker and FileVault), firewall rules, attack surface reduction (ASR), and account protection.
Intune also integrates with Microsoft Defender for Endpoint (MDE), allowing administrators to onboard devices, use device risk information in compliance policies, and manage supported security settings. However, Intune and Defender for Endpoint serve different purposes. Intune focuses on device management and security configuration, while Defender for Endpoint provides advanced threat detection, investigation, and response capabilities. Defender for Endpoint may require a separate license, depending on your existing Microsoft subscriptions.
When creating security policies in Intune, make sure the same setting is not configured with different values across multiple policies. For example, a setting configured through a security baseline, endpoint security policy, or device configuration profile could cause conflicts if different values are applied to the same device. To avoid this, plan your policies carefully and decide which policy will manage each security setting.
Refer to the link to read more about Endpoint security policies: Endpoint security in Microsoft Intune – Microsoft Intune | Microsoft Learn.
5. Device Compliance and Conditional Access
Microsoft Intune allows IT administrators to create device compliance policies to check whether managed devices meet the organisation’s security requirements. For example, you can check whether a device has disk encryption enabled, a supported operating system version, a password configured, or other required security settings.
Intune can also work with Microsoft Entra Conditional Access to control access to company resources based on device compliance status. For example, you can create a Conditional Access policy that allows users to access Microsoft 365 applications only when their devices are marked as compliant in Intune.
It is important to understand that Intune and Conditional Access perform different tasks. Intune evaluates whether a device meets the configured compliance requirements, while Conditional Access uses that information to allow or block access to company resources. Simply creating a compliance policy in Intune does not automatically restrict access. You must also configure the appropriate Conditional Access policy in Microsoft Entra.
Before implementing these policies, check the Microsoft Entra licensing requirements and test the configuration with a small group of users and devices. This helps you identify potential sign-in issues and ensure that legitimate users are not unexpectedly blocked from accessing company resources.
Learn more about integration between conditional access and Intune here: Use Conditional Access with Microsoft Intune compliance policies – Microsoft Intune | Microsoft Learn
6. Windows Autopilot and Autopilot Device Preparation
Windows Autopilot simplifies the process of setting up and deploying Windows devices in an organisation. Instead of manually installing Windows using custom images and configuring each device, IT administrators can use Windows Autopilot with Microsoft Intune to automatically enroll devices, apply configuration policies, and install required applications during the initial setup. This helps reduce manual work and allows users to get their devices ready for business use with minimal IT involvement.
Microsoft also provides Windows Autopilot device preparation, which offers another way to set up and configure Windows devices. Although both solutions help automate device provisioning, they have different requirements, supported scenarios, and capabilities. Therefore, it is important to understand these differences before choosing the appropriate deployment method for your organisation.
When testing Windows Autopilot, make sure you verify the complete device setup process, including user sign-in, Intune enrollment, application installation, and configuration policy deployment. A successful deployment should ensure that the device is properly configured and that users have access to the applications and settings they need to start working.
Below are some of my step-by-step guides to help you get started with Windows Autopilot:
7. Windows Update Management
Intune provides several policy types for managing Windows updates:
| Policy | Purpose |
|---|---|
| Update rings | Control update behaviour, including deferrals, deadlines, and restarts. |
| Feature updates | Target a Windows feature release and control upgrades. |
| Quality updates | Manage supported monthly security and reliability update scenarios. |
| Expedite policies | Accelerate supported security updates. |
| Driver updates | Control deployment of drivers offered through Windows Update. |
Microsoft Intune allows IT administrators to manage Windows updates by configuring update ring policies, feature update policies, quality update policies, and other supported update settings. The actual update files are downloaded from Windows Update, while Intune controls how and when updates are offered and installed on managed devices.
Intune also integrates with Windows Autopatch, which provides additional capabilities to automate and manage Windows updates, helping organisations keep their devices up to date with less manual effort.
Before deploying updates to all devices, start with a small test group to verify that updates install successfully and do not cause compatibility issues with existing applications or configurations. You should also check the prerequisites and licensing requirements for each update feature, especially advanced capabilities such as hotpatch updates, which are supported only on eligible devices that meet specific requirements.
Below are some of my step-by-step guides to help you get started with managing Windows updates using Microsoft Intune.
8. Advanced endpoint management
Microsoft Intune also provides advanced features that help IT administrators with device support, security, and management tasks. Before using these features, check their supported platforms, prerequisites, and licensing requirements. Just because a feature is visible in the Intune admin center does not necessarily mean that all users or devices are eligible or licensed to use it.
| Capability | Main purpose |
|---|---|
| Remote Help | Provide remote support with administrative access controls. |
| Endpoint Privilege Management | Allow approved elevated tasks while users retain standard accounts. |
| Advanced Analytics | Investigate endpoint experience and performance. |
| Enterprise Application Management | Deploy curated Win32 applications from Microsoft’s hosted catalog. |
| Microsoft Tunnel for MAM | Provide supported unenrolled mobile apps with access through Microsoft Tunnel. |
| Specialty device management | Manage supported specialist device categories. |
| Firmware Over-the-Air updates | Deliver supported Android firmware updates remotely. |
9. Microsoft Cloud PKI
Microsoft Cloud PKI is a cloud-based certificate management solution that allows IT administrators to issue, renew, and revoke certificates for supported Intune-managed devices. It helps reduce the need to maintain traditional on-premises Public Key Infrastructure (PKI) servers by hosting the certificate authority (CA) and related services in the cloud.
Cloud PKI supports Windows, macOS, iOS/iPadOS, and Android devices. Devices must be enrolled in Intune and support the required SCEP certificate profile to receive certificates. These certificates can be used for scenarios such as certificate-based authentication to corporate Wi-Fi networks, VPN connections, and other supported services.
Although Microsoft Cloud PKI simplifies certificate management, it is not a complete replacement for every traditional PKI solution. Before moving to Cloud PKI, review your organisation’s certificate requirements, trusted certificate configurations, supported authentication scenarios, and licensing requirements to ensure it meets your needs.
Learn more about Microsoft Cloud PKI in Intune here: Microsoft Cloud PKI for Microsoft Intune – Microsoft Intune | Microsoft Learn.
10. Microsoft Copilot in Intune
Microsoft Copilot in Intune, powered by Microsoft Security Copilot, helps IT administrators manage and troubleshoot devices more efficiently using AI. It can help administrators understand configuration policies, review security settings, analyze device information, and identify potential issues. Instead of manually checking multiple settings and reports, administrators can use Copilot to get useful insights and recommendations.
To use Copilot in Intune, your organisation must meet the Microsoft Security Copilot requirements, including the appropriate configuration, capacity, permissions, and access to the Intune data source. Copilot also follows the administrator’s existing Intune role-based access control (RBAC) permissions and scope tags, ensuring that administrators can only access information they are authorized to view.
Microsoft also provides specialized AI agents for tasks such as policy configuration and vulnerability remediation. These agents can help administrators identify issues and recommend actions, but their availability, licensing, and prerequisites may differ. For example, vulnerability remediation capabilities may require additional Microsoft Defender features.
Although Copilot can save time and simplify administration, AI-generated recommendations should always be reviewed before applying changes, especially when modifying security policies, access controls, or settings that could affect a large number of devices.
Learn more about Copilot:
11. Deployments and Deployment Plans in Intune
Deployments and Deployment Plans in Microsoft Intune help IT administrators automate the phased rollout of applications and policies to different groups of users or devices. A Deployment Plan defines the deployment rings, Microsoft Entra security groups, exclusions, rollout sequence, and wait time between each ring.
A Deployment uses this plan to assign a selected application or policy (payload) to the configured groups automatically based on the defined schedule. This feature reduces the need to manually update assignments for each deployment phase and provides options to monitor, pause, resume, or cancel deployments.
An important point to understand is that deployments are time-based rather than success-based, meaning the rollout progresses according to the configured schedule, regardless of whether the previous ring was successful. You must monitor deployment results and manually pause the rollout if issues are identified.
Learn more about Deployments and Deployment Plans here: Deployments And Deployment Plans In Intune.
Microsoft Intune Pricing
The table below shows the Microsoft-published US pricing in USD per user per month. Add-on prices are based on annual billing. Actual prices may vary depending on your country or region, applicable taxes, licensing agreements, and purchase terms.
Advanced Intune add-ons require a Microsoft Intune Plan 1 license. Before purchasing additional licenses, check your existing Microsoft subscription to ensure that the required features are not already included. This helps avoid paying twice for the same capabilities.
| Product | Price |
|---|---|
| Intune Plan 1 | $8.00 |
| Intune Plan 2 add-on | $4.00 |
| Intune Suite add-on | $10.00 |
| Remote Help | $3.50 |
| Endpoint Privilege Management | $3.00 |
| Advanced Analytics | $5.00 |
| Enterprise Application Management | $2.00 |
| Microsoft Cloud PKI | $2.00 |
| Microsoft Intune Plan 1 ($8/user/month) |
| Cloud-based UEM solution with basic functionalities such as: ✔️ Endpoint Management of Windows, Android, iOS, and macOS devices. ✔️ Endpoint security ✔️ Endpoint Analytics ✔️ Mobile Application Management [MAM] Intune Plan 1 is included in: ✔️ Microsoft 365 E3, E5, F1, F3, Enterprise Mobility + Security E3 and E5, and Business Premium plans. |
| Microsoft Intune Plan 2 ($4/user/month) |
| This is an add-on license to Microsoft Intune Plan 1 which provides Advanced endpoint management. Along with that, It includes: ✔️ Microsoft Intune Tunnel for MAM ✔️ Endpoint Management of Speciality Devices ✔️ Mobile firmware updates over-the-air |
| Microsoft Intune Suite ($10/user/month) |
| It is also an add-on to the Microsoft Intune Plan 1 license. Below additional functionality/tools are included in the Intune Suite: ✔️ Remote Help ✔️ Endpoint Privilege Management ✔️ Intune Advanced Analytics ✔️ Microsoft Cloud PKI ✔️ Microsoft Enterprise App Managment |
| Intune Standalone Licenses | Price (USD per user/month, paid yearly) |
|---|---|
| Intune Remote Help | $3.50 |
| Endpoint Privilege Management | $3.00 |
| Enterprise App Management | $2.00 |
| Advanced Analytics | $5.00 |
| Cloud PKI | $2.00 |
Each add-on requires Microsoft Intune Plan 1, purchased separately or included in an eligible subscription. Prices may vary by region and agreement. Before purchasing, check your existing Microsoft 365 E3 or E5 entitlements, as Microsoft began rolling advanced Intune capabilities into these subscriptions in July 2026.
Microsoft 365 E3 and E5 Licensing Changes
Starting in July 2026, Microsoft began rolling out additional Microsoft Intune capabilities to organizations with Microsoft 365 E3 and E5 subscriptions. These changes provide access to more advanced Intune features without requiring separate add-on licenses for the included capabilities.
| Subscription | Additional Intune capabilities |
|---|---|
| Microsoft 365 E3 | Remote Help, Advanced Analytics, and Intune Plan 2 capabilities. |
| Microsoft 365 E5 | All the additional E3 capabilities, plus Endpoint Privilege Management, Cloud PKI, and Enterprise Application Management. |
Organizations will receive a 30-day notice through the Microsoft 365 Message Center before these features are activated in their tenant. Before purchasing additional Intune licenses, check your existing Microsoft 365 subscription and Message Center notifications to confirm which features are already included and available in your tenant.
These licensing changes apply to eligible Microsoft 365 E3 and E5 subscriptions. Do not assume that Office 365 E3/E5 or Enterprise Mobility + Security (EMS) subscriptions include the same additional Intune capabilities. Refer to this link to understand about Intune pricing Microsoft Intune Pricing | Microsoft Security.
Other Licensing Considerations
Microsoft Intune Suite is an add-on to Intune Plan 1 and includes the capabilities of Intune Plan 2, along with additional advanced features. Many organizations already have Intune Plan 1 through their Microsoft 365 subscriptions, so it is important to review your existing licenses before purchasing standalone plans or add-ons.
Microsoft also offers device-only licensing for devices that are not assigned to a specific user, such as kiosks, shared devices, and dedicated devices. However, device-only licensing is different from user-based licensing and does not support certain features, such as app protection policies, conditional access, and other user-based management capabilities. Make sure you select the appropriate licensing model based on how your devices will be used.
To check your Intune licensing information, sign in to the Intune admin center and navigate to Tenant administration > Tenant status. This page provides tenant information, including license counts. You should also check the licenses assigned to individual users in the Microsoft 365 admin center to confirm they have the required licenses for the Intune features you plan to use.
Refer to this link to know more about Intune licensing, Microsoft Intune Licensing Plans and Options – Microsoft Intune | Microsoft Learn.
Frequently Asked Questions
Can Intune protect apps without enrolling a device?
Yes. Microsoft Intune supports Mobile Application Management (MAM), which allows IT administrators to protect corporate data within supported applications without enrolling the device in Intune. This is particularly useful for personally owned devices (BYOD) where users need access to company applications such as Outlook and Teams without allowing IT to manage their entire device.
Does Intune replace Microsoft Defender for Endpoint?
No. Microsoft Intune and Microsoft Defender for Endpoint (MDE) serve different purposes but can work together. Intune focuses on device management, configuration policies, compliance, and application deployment. Defender for Endpoint provides advanced security capabilities such as threat detection, investigation, and response. Defender for Endpoint may require additional licensing depending on your Microsoft subscription.
Does every device support the same Intune features?
No. Intune features vary depending on the device platform, operating system version, edition, and enrollment method. For example, certain Windows management features may not be available on macOS, iOS, or Android devices. Before deploying a feature, check Microsoft’s documentation to confirm that it is supported on your devices.
Should I buy Intune Suite immediately?
Not necessarily. Before purchasing Microsoft Intune Suite, review your existing Microsoft 365 and Intune licenses to identify which features are already included. Make a list of the advanced capabilities your organization needs, such as Remote Help, Endpoint Privilege Management, or Cloud PKI. Then compare the cost of purchasing individual add-ons against Intune Suite. It is also recommended to test the required features with a small group of users and devices before making a purchasing decision.